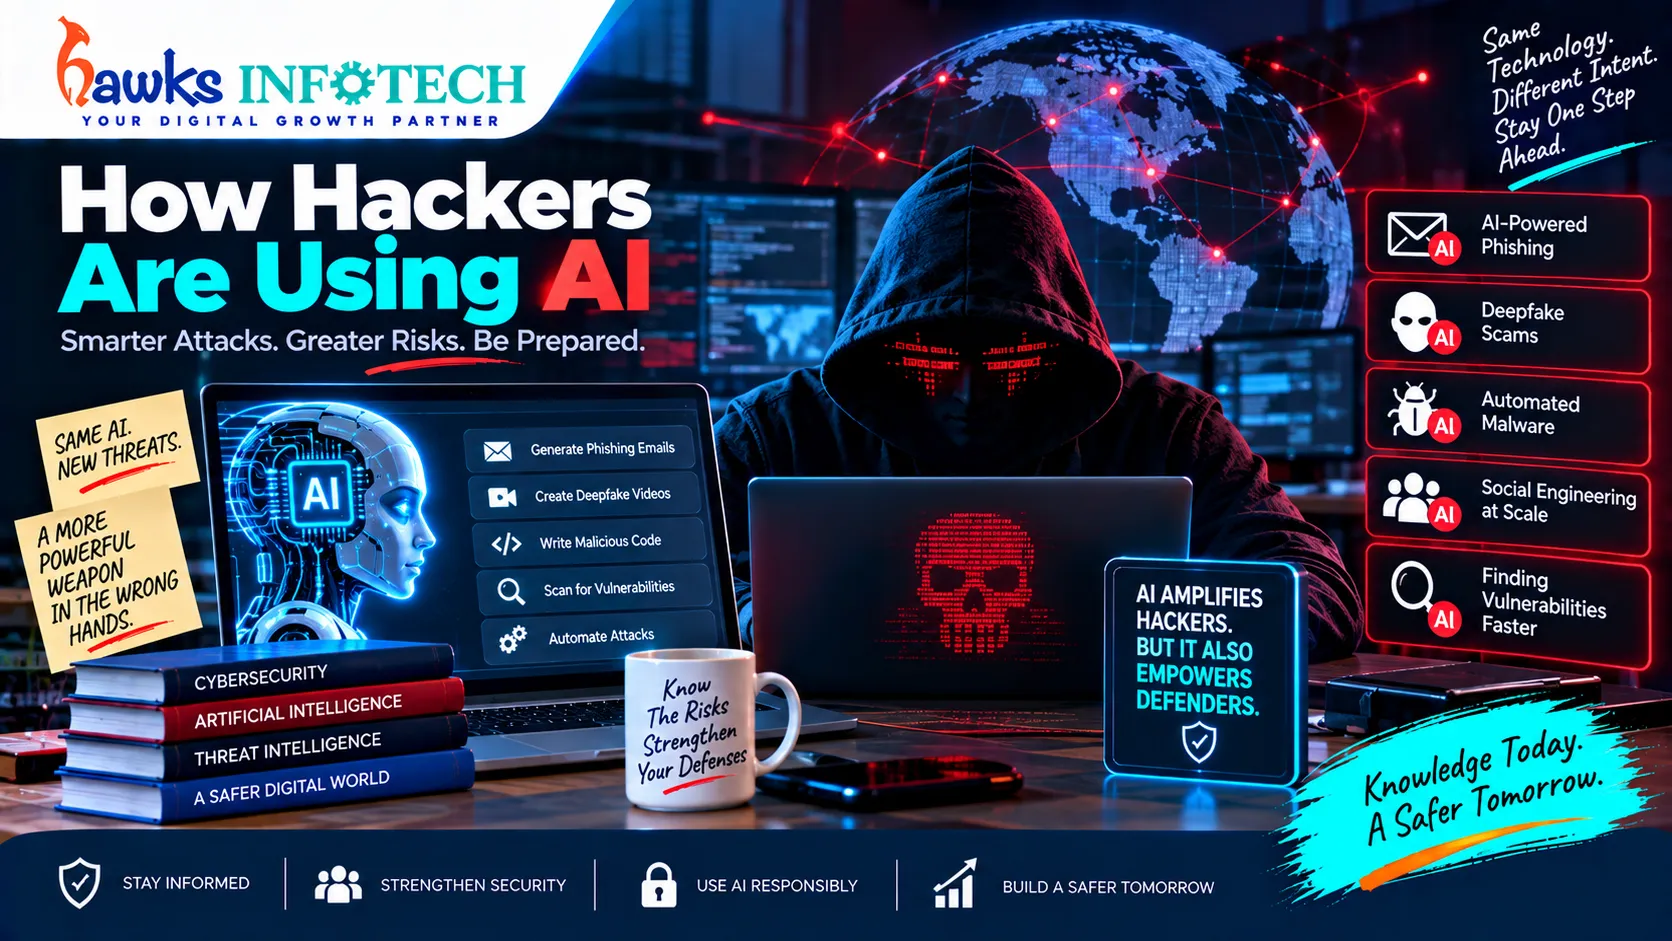
To defeat a sophisticated adversary, you must understand their tradecraft. In 2026, the stereotype of a lone hacker typing green code in a dark basement has been replaced by organized, highly capitalized cyber syndicates operating like modern tech startups. These criminal syndicates deploy fine-tuned, uncensored large language models—known on the dark web as WormGPT, FraudGPT, and DarkBERT—to automate reconnaissance, discover zero-day vulnerabilities, crack multi-factor challenges, and orchestrate precision attacks at machine speed.
Cybercrime-as-a-Service
Novice criminals purchase turnkey AI subscriptions that generate functional exploits, bypass email filters, and manage ransomware ransom negotiations automatically.
Defensive Imperative
Static perimeter firewalls are obsolete. Security teams must implement behavioral threat correlation and autonomous incident isolation to withstand machine attacks.
Supporting Deep-Dive Guide
Master Pillar: AI-Powered Cybersecurity Threats in 2026
Table of Contents
Direct Answer: How are hackers using AI in 2026?
In 2026, hackers use artificial intelligence to: 1) Deploy uncensored LLMs for writing context-aware phishing lures, 2) Automate vulnerability discovery in proprietary web applications, 3) Clone executive voices and video for wire fraud, 4) Write self-mutating polymorphic code that evades antivirus signatures, and 5) Orchestrate botnets that mimic human browsing to bypass fraud filters.
1. The Rise of Black-Hat AI Models: WormGPT, FraudGPT, and Beyond
While ethical technology companies implement safety guardrails on public models (such as ChatGPT, Claude, and Gemini) to prevent generating malicious code, threat actors have developed their own specialized neural networks.
Hosted on bulletproof dark web infrastructure, these underground models are fine-tuned specifically on repository dumps of malware source code, leaked exploit frameworks, and dark web forum communications:
- They generate functional keylogger and ransomware code upon simple natural language prompts.
- They analyze security vendor whitepapers to identify undisclosed weaknesses in commercial antivirus software.
- They craft hyper-targeted spear-phishing templates customized by industry vertical and geography, as detailed in our guide on AI-powered phishing.
2. Automated Reconnaissance & Attack Surface Mapping
Before an adversary strikes, they conduct reconnaissance. In previous years, mapping a target company's internet attack surface required hours of manual Shodan searches, DNS enumeration, and employee profiling.
Today, AI agents execute autonomous reconnaissance in under 90 seconds:
- The bot crawls your company's domain, identifying subdomains, development staging servers, and open API ports.
- It correlates employee email addresses with public database breach dumps, identifying reused passwords.
- It scans corporate LinkedIn profiles to determine what software versions (e.g. outdated VPN appliances, unpatched ERP systems) your company operates.
This speed mirrors the broader threat trends we outlined in AI-powered cybersecurity threats in 2026.
3. AI-Powered Vulnerability Fuzzing & Exploit Generation
Software vulnerability fuzzing involves sending random, invalid data into applications to discover buffer overflows or memory leaks. Historically, fuzzing was a brute-force guessing game requiring substantial compute and days of trial and error.
In 2026, adversaries employ smart neural fuzzers. The AI analyzes web application responses, predicts which input structures are most likely to trigger backend database syntax exceptions, and autonomously constructs functional SQL injection or remote code execution payloads tailored to that specific application architecture.
Beyond application binaries, attackers use AI to orchestrate distributed credential stuffing against exposed enterprise APIs. By modeling human keyboard typing speeds, introducing randomized network latency, and rotating residential IP addresses dynamically, automated bots defeat legacy rate limiting and CAPTCHAs, unlocking corporate accounts without triggering security sirens.
4. Autonomous Evasion: Bypassing EDR & Firewalls
Modern malware does not just execute; it actively evades detection using machine learning algorithms:
Sandbox Detection
The malware checks mouse movement vectors, recent document histories, and hardware clock drift to confirm it is running on a real human workstation rather than an analyst virtual machine.
Polymorphic Assembly
The binary rearranges function orders and inserts harmless system API calls upon every execution, rendering static antivirus signatures obsolete.
Living-off-the-Land
The malware avoids downloading suspicious external binaries, instead using legitimate administrative tools (PowerShell, WMI) to accomplish its objectives.
5. Social Engineering Automation & Deepfakes
The most alarming weaponization of AI is synthetic social engineering. Attackers combine conversational language models with generative voice and video synthesis:
- Synthetic Audio Cloning: Threat syndicates clone corporate executive voices using public podcast interviews or conference appearances to authorize emergency wire transfers. Learn more in AI voice scams and business security.
- Executive Deepfake Video Calls: Attackers join corporate video calls using synthetic avatars to impersonate senior partners and board members. Explore localized case studies in deepfake fraud and Indian businesses.
6. Defensive Playbook: Neutralizing Offensive AI
To protect corporate infrastructure against machine-speed attacks, small and enterprise businesses must implement defense-in-depth:
- Deploy Behavioral Endpoint Telemetry: Upgrade legacy antivirus software to modern EDR/XDR agents capable of isolating anomalous process behavior in real time. (See our guide on AI cybersecurity for small businesses).
- Enforce Strict Out-of-Band Verification: Never allow financial disbursements or critical infrastructure changes based on email, chat, or inbound phone calls alone.
- Continuous Proactive Monitoring: Partner with a managed operations center providing 24/7 proactive monitoring, as outlined in our overview of AI-powered IT support.
7. Frequently Asked Questions
Can ethical AI models like ChatGPT be used by hackers directly?
Public commercial AI models have extensive safety filters that block malicious prompts. However, threat actors often use sophisticated "jailbreak" prompts to bypass these guardrails or operate self-hosted open-source language models with safety restrictions completely removed.
How do hackers get samples of an executive's voice to clone it?
With modern voice cloning technology, an attacker only requires 3 to 10 seconds of clear audio. They scrape this audio from YouTube interviews, corporate webinar recordings, media appearances, or by initiating a casual cold call and recording the executive's voice response.
What is the best way to test our company's vulnerability to AI hackers?
Commission an AI-driven penetration test and red-team assessment. Ethical security firms simulate realistic AI attacks—including voice cloning, simulated spear-phishing, and external attack surface audits—to identify vulnerabilities before real criminals exploit them.
Topical Cluster: AI-Powered Cybersecurity & Threat Defense
Explore the complete interconnected network of pillar guides and specialized deep-dive articles in this domain:

AI-Powered Cybersecurity Threats in 2026
Explore the comprehensive master guide that unifies all AI-Powered Cybersecurity & Threat Defense strategies.


